The Three Questions That Change What a Board Actually Knows
Board Cyber Governance Keynote Speaker
A 2025 Gartner survey of non-executive directors found that 90 percent lack confidence their organization has the right balance of cybersecurity protection and cost, even though those same boards approve the budgets, sit through the quarterly briefings, and sign off on the risk appetite statements every year. The oversight machinery is running. It is not producing the thing boards think it produces. Mark Lynd is a board cyber governance keynote speaker who briefs boards from the seat of someone who has built and delivered the reporting a board actually receives, not studied it from the outside. He is a 5x CEO/CIO/CISO with Thinkers360 Top 10 global rankings across Cybersecurity and Artificial Intelligence, was ranked #1 globally in Cybersecurity in 2023, and currently leads Executive Advisory and Strategy at Netsync, advising enterprise boards on the cybersecurity and AI questions moving fastest in 2026. A 2026 benchmark report from IANS, Artico Search, and the CAP Group, drawing on 17 board directors and a separate survey of 663 CISOs, found the shape of the problem precisely: 95 percent of CISOs deliver regular board updates, and 82 percent of directors rate the regulatory-reporting content as satisfactory or better, but only 47 percent felt satisfied with the CISO's ability to articulate the impact of a given threat. Compliance reporting is solid. Forward-looking risk judgment is thin, and the same report found security updates get roughly 30 minutes of average board airtime, with 35 percent of boards restricting CISO engagement to a committee rather than the full board. The talk is built around the Three Questions framework: what is the single biggest way we could be breached in the next twelve months, and what stands between us and that outcome today; if that answer got worse, would we know, and how; and what did we decide not to fix, and why. Asked consistently, quarter after quarter, these three questions force a board's reporting format to shift from a scorecard of control existence to an honest account of risk trend, the distinction that mattered in a real mid-cap financial services board engagement where two years of green quarterly scorecards preceded a third-party vendor breach the scorecard had never been built to catch.
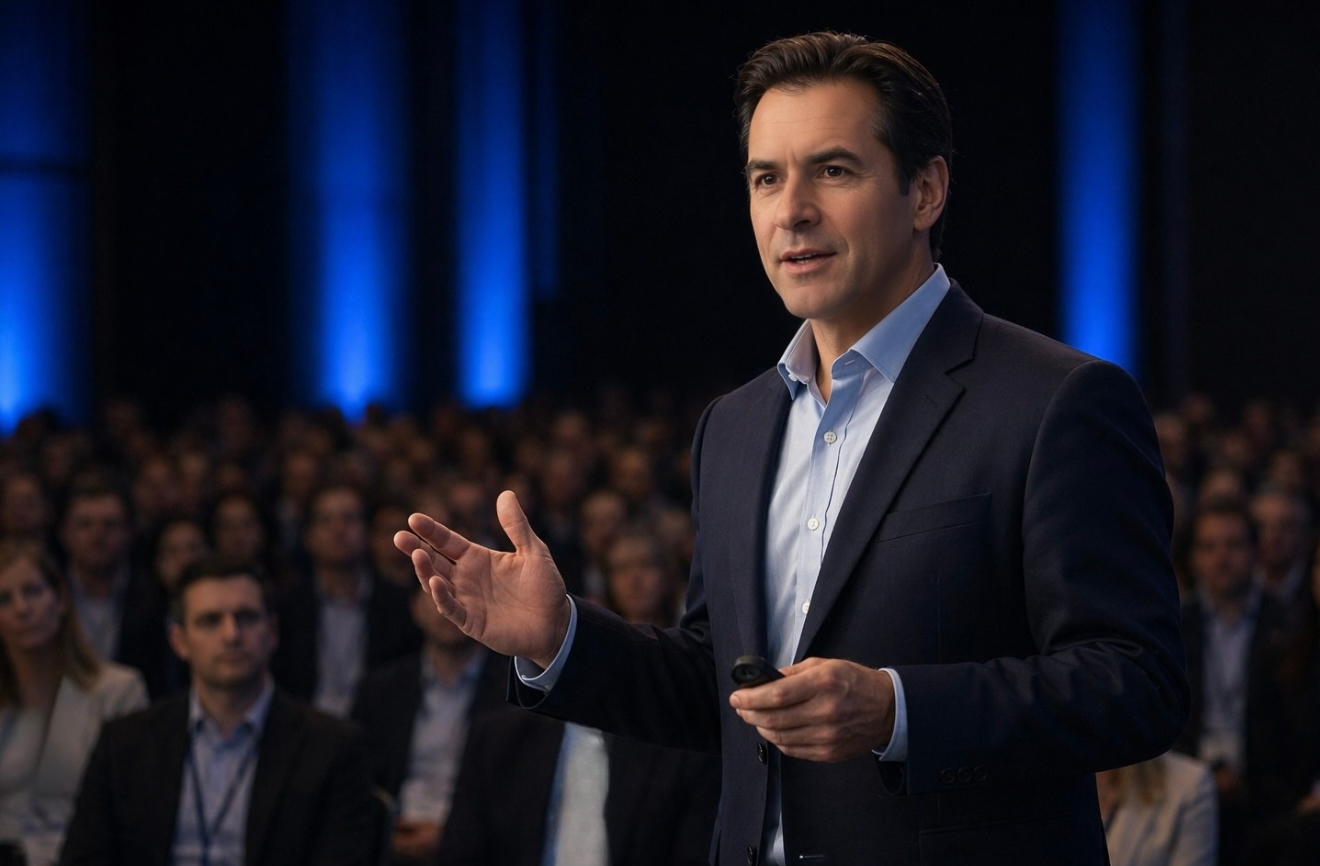
Live on stage · International keynote
Quick Answer
A 2025 Gartner survey of non-executive directors found that 90 percent lack confidence their organization has the right balance of cybersecurity protection and cost, even though those same boards approve the budgets, sit through the quarterly briefings, and sign off on the risk appetite statements every year.
Keynote Topics
What Boards Get Wrong About Cybersecurity Oversight
Why quarterly scorecards, compliance attestations, and green-yellow-red dashboards give boards comfort without giving them an answer to the question that matters: is the organization's risk exposure trending up or down. Grounded in 2025-2026 Gartner and IANS/Artico/CAP Group board-governance research.
Best for: Board, audit committee, and C-Suite audiences
Duration: 45-90 minutes
The Three Questions Framework Deep Dive
A practitioner-level session for CISOs and their teams on building board reporting around three questions: the single biggest breach exposure and what stands between the organization and it, whether deterioration would actually be detected, and what has been deliberately left unfixed and why.
Best for: CISOs and security leadership preparing board reporting
Duration: 45-90 minutes
Board Briefing: Are We Actually Safer This Quarter
A 30-60 minute board-level briefing that walks directors through the Three Questions framework directly, structured so the board leaves with the specific follow-up questions to ask their own CISO at the next quarterly update.
Best for: Board events, audit committee sessions, governance summits
Duration: 30-60 minutes
I don't give speeches. I bring the view from the frontlines, what I'm actually seeing this quarter running enterprise AI and cybersecurity programs and advising boards, so your audience leaves with something real.
Mark Lynd, 5x CEO/CIO/CISO, Head of Executive Advisory & Strategy at Netsync
Why Boards Choose Mark Lynd as Their Cyber Governance Keynote Speaker
He has built the reporting a board actually receives. 5x CEO/CIO/CISO, currently Head of Executive Advisory and Strategy at Netsync, including current board-advisory engagements this year.
Verified Top 10 global rankings across Cybersecurity and Artificial Intelligence on Thinkers360. Cybersecurity, Artificial Intelligence, Cloud, Security, and Data Center, held simultaneously. Ranked #1 Global Cybersecurity Thought Leader for 2023.
A named framework grounded in current research, not a generic checklist. The Three Questions framework is built directly from 2025-2026 Gartner and IANS/Artico Search/CAP Group board-governance survey data, plus a real advisory engagement where it exposed a gap a passing scorecard had missed.
US Army veteran, three published books, two weekly newsletters. 3rd Ranger Battalion and 82nd Airborne Division. A Leader's Playbook for Cyber Insurance, Cyber War: One Scenario, Cybersecurity Life Skills for Teens, plus the Hype Check Now newsletter.
Speaker Reel
Watch Mark on Stage
A sampling of keynotes, panels, and live broadcast appearances, RSA, Oracle CloudWorld, Dell Technologies World, ESPN College Football Awards, and the Technology Ball.
What Audiences Say
Feedback From Event Hosts and C-Suites
Mark stands apart. His credibility isn’t rooted in a title from years ago, it’s built through the work he’s doing every day in the field. When he speaks about our technology, enterprise buyers pay attention because they know his perspective is grounded in real-world experience.
Shira Rubinoff
CEO, The Cybersphere Group
Mark delivers more than a presentation, he delivers operational insight from the front lines. Instead of theory, he shares what is actually working in real environments. Our audience of CISOs and security leaders left with practical strategies they could begin implementing immediately.
Jo Peterson
CIO, Clarify360
Where Has Mark Spoken?
According to venue records, Mark has delivered keynotes at: RSA Conference · Oracle CloudWorld · Cisco Partner Summit · Dell Technologies World · IBM Think · T-Mobile Events · Gartner Security & Risk · InfoSecurity · ISACA Conferences · ISSA Events · Cloud Security Alliance · CyberSecurity Summit · BSides · FLGISA · MISAC · SMU Cox School of Business · and 100+ more.
How Do You Book Mark Lynd for Your Event?
The booking process is straightforward and typically completes within 3 business days. Mark customizes every keynote to the audience, industry, and event objectives.
- Submit an inquiry. Fill out the contact form with your event date, audience, and objectives. Response within 48 hours.
- 15-minute discovery call. Discuss your event in detail, including audience makeup, key messages, and desired outcomes.
- Proposal & contract. Receive a tailored proposal with format options (keynote, workshop, panel), fee, and travel terms.
- Customization. Mark customizes content to your audience, industry examples, and desired takeaways.
- Expert delivery. Mark brings 25+ years of real-world executive experience to every stage.
Frequently Asked Questions
What is the Three Questions framework?
How is this different from a standard board cybersecurity briefing?
What data is this based on?
What does it cost to book Mark Lynd?
Does Mark customize the talk to our board?
Ready to Book Mark?
Mark customizes every keynote to the audience, industry, and event objectives. Contact the booking team to check availability.
600+ projects, keynotes, panels and workshops · audiences from 50 to 5,000+
Formats: In-person, virtual, hybrid · international available
Duration: 30–120 minutes depending on format
Custom by event · educational pricing available
Related speaking services
Board Advisor for AI & Cyber Risk · AI Agents Security Keynote Speaker · Keynote Speaker the U.S. (All Topics)